
Skip to content
PamStealer Uses Fake Maccy Sites and PAM Checks to Steal Mac Login Passwords

PamStealer Uses Fake Maccy Sites and PAM Checks to Steal Mac Login Passwords

Cybersecurity researchers have flagged a new macOS information stealer called PamStealer that employs a series of clever tricks to infect systems and siphon sensitive data. The stealer, discovered by Jamf Threat Labs, is distributed as a compiled AppleScript (.scpt) file impersonating Maccy, a legitimate open-source clipboard manager. It has beenRead More »PamStealer Uses Fake Maccy Sites and PAM Checks to Steal Mac Login Passwords
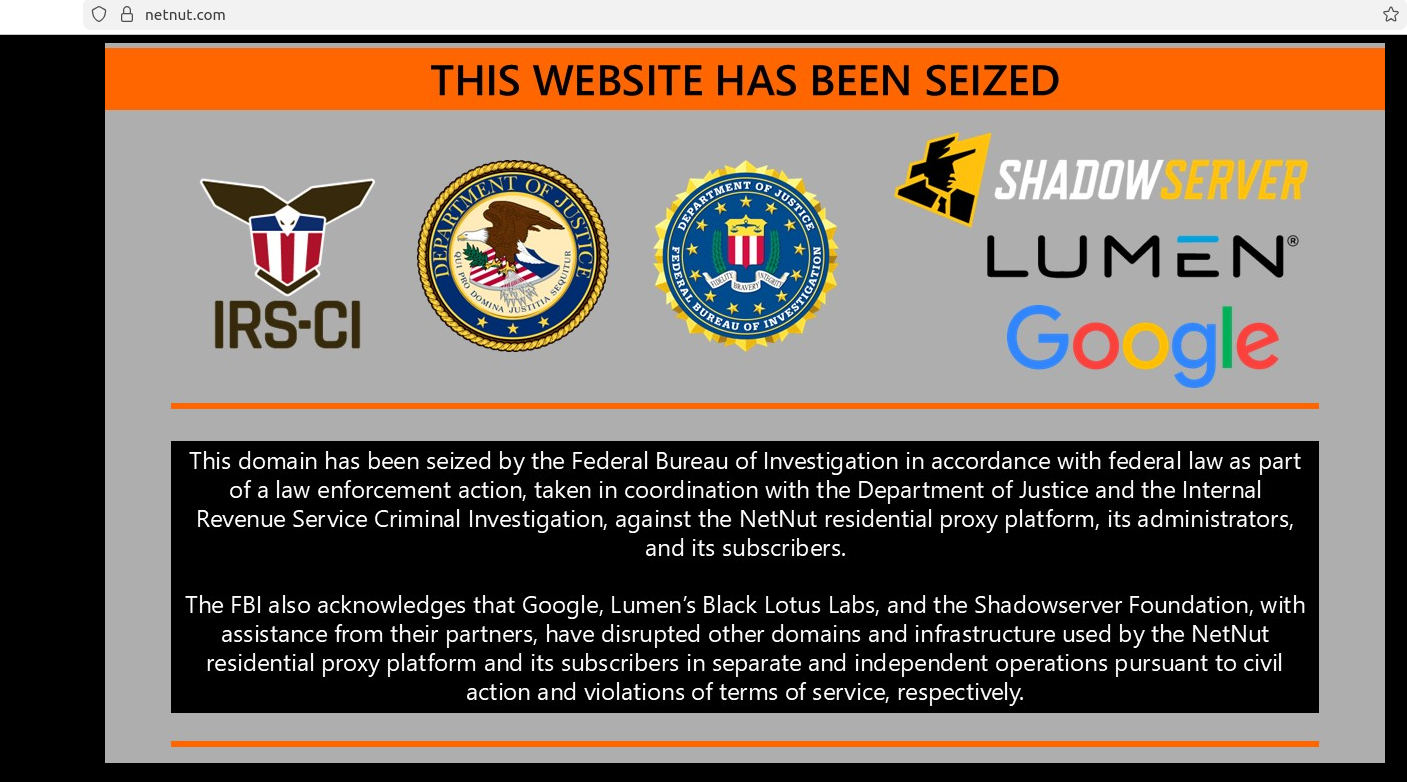
Google Disrupts NetNut Residential Proxy Network Spanning 2 Million Home Devices

Google Disrupts NetNut Residential Proxy Network Spanning 2 Million Home Devices

Google has significantly degraded NetNut, one of the biggest networks that turns home devices into rented relays for other people’s traffic. Working with the FBI, Lumen, and others, Google’s Threat Intelligence Group (GTIG) said this week it had reduced the network’s pool of usable devices by millions. Google identifies NetNut, also trackedRead More »Google Disrupts NetNut Residential Proxy Network Spanning 2 Million Home Devices

Ransomware Groups Turn to Citrix Bleed 2, BYOVD, and Supply Chain Credentials

Ransomware Groups Turn to Citrix Bleed 2, BYOVD, and Supply Chain Credentials

Threat actors associated with the Anubis ransomware operation have been observed exploiting the Citrix Bleed 2 (CVE-2025-5777) vulnerability to obtain initial access. “Although tactics differ between affiliates, common patterns emerged in tradecraft through use of legitimate Remote Management and Monitoring (RMM) tooling, credential access, and hands-on-keyboard procedures used for lateral

How to Conduct a Successful Audit of AI-Driven Software Development

As AI-generated code becomes commonplace, CISOs need new audit strategies to measure developer practices, govern AI tool usage, and identify software risks before they reach production. The post How to Conduct a Successful Audit of AI-Driven Software Development appeared first on SecurityWeek.

ToddyCat-Linked Umbrij Malware Abuses OAuth to Access Gmail via Google API

ToddyCat-Linked Umbrij Malware Abuses OAuth to Access Gmail via Google API

The threat actor known as ToddyCat has been attributed to a new malware called Umbrij that’s designed to gain surreptitious access to a victim’s email correspondence via the Google API. “In this campaign, the attackers focused their attention on corporate email communications hosted on Gmail, targeting access compromise via APIs,”Read More »ToddyCat-Linked Umbrij Malware Abuses OAuth to Access Gmail via Google API

Copyright © 2026 infosecintel.net