
How to Stay Safe Online This Black Friday, According to a Cyber Expert
A cyber expert shares how individuals — and organizations — can stay safe during the holiday shopping season.
A cyber expert shares how individuals — and organizations — can stay safe during the holiday shopping season.

Gainsight has disclosed that the recent suspicious activity targeting its applications has affected more customers than previously thought. The company said Salesforce initially provided a list of 3 impacted customers and that it has “expanded to a larger list” as of November 21, 2025. It did not reveal the exactRead More »Gainsight Expands Impacted Customer List Following Salesforce Security Alert
Shai-hulud 2.0 campaign features a sophisticated variant capable of stealing credentials and secrets from major cloud platforms and developer services, while automating the backdooring of NPM packages maintained by victims. Its advanced tactics enable rapid, stealthy propagation across the software supply chain, putting countless downstream users at risk.

The second wave of the Shai-Hulud supply chain attack has spilled over to the Maven ecosystem after compromising more than 830 packages in the npm registry. The Socket Research Team said it identified a Maven Central package named org.mvnpm:posthog-node:4.18.1 that embeds the same two components associated with Sha1-Hulud: the “setup_bun.js”Read More »Shai-Hulud v2 Campaign Spreads From npm to Maven, Exposing Thousands of Secrets
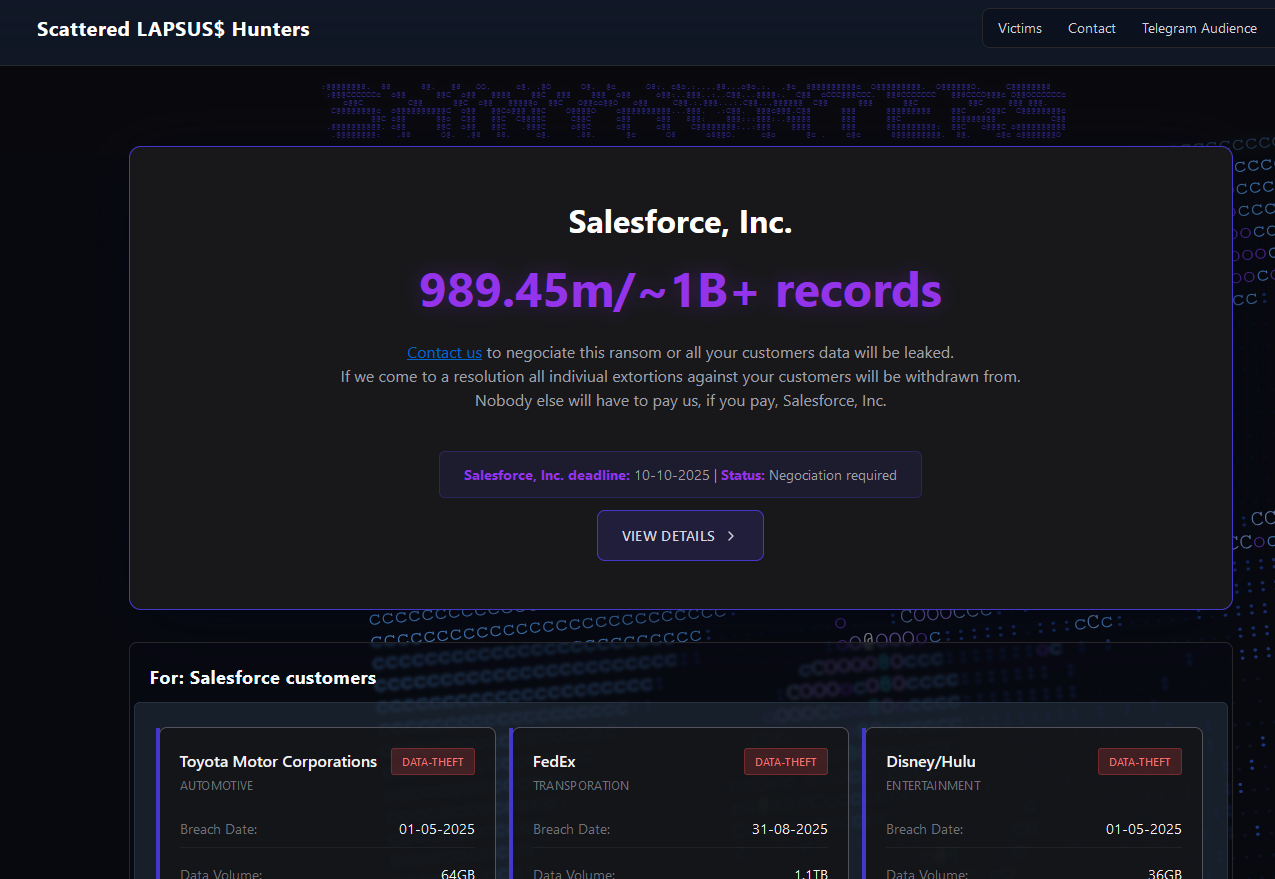
A prolific cybercriminal group that calls itself “Scattered LAPSUS$ Hunters” has dominated headlines this year by regularly stealing data from and publicly mass extorting dozens of major corporations. But the tables seem to have turned somewhat for “Rey,” the moniker chosen by the technical operator and public face of theRead More »Meet Rey, the Admin of ‘Scattered Lapsus$ Hunters’

South Korea’s financial sector has been targeted by what has been described as a sophisticated supply chain attack that led to the deployment of Qilin ransomware. “This operation combined the capabilities of a major Ransomware-as-a-Service (RaaS) group, Qilin, with potential involvement from North Korean state-affiliated actors (Moonstone Sleet), leveraging ManagedRead More »Qilin Ransomware Turns South Korean MSP Breach Into 28-Victim ‘Korean Leaks’ Data Heist
The cybersecurity startup embeds AI agents into widely used tools to identify design flaws and eliminate them early. The post Clover Security Raises $36 Million to Secure Software by Design appeared first on SecurityWeek.
Cybercriminals impersonating financial institutions have targeted individuals, businesses, and organizations of different sizes. The post Account Takeover Fraud Caused $262 Million in Losses in 2025: FBI appeared first on SecurityWeek.
JSONFormatter and CodeBeautify users exposed credentials, authentication keys, configuration information, private keys, and other secrets. The post Thousands of Secrets Leaked on Code Formatting Platforms appeared first on SecurityWeek.
This quote is from House of Huawei: The Secret History of China’s Most Powerful Company. “Long before anyone had heard of Ren Zhengfei or Huawei, Wan Runnan had been China’s star entrepreneur in the 1980s, with his company, the Stone Group, touted as “China’s IBM.” Wan had believed that economicRead More »Huawei and Chinese Surveillance