
Hackers Target Casino Operator Boyd Gaming
Boyd Gaming has informed the SEC about a data breach affecting the information of employees and other individuals. The post Hackers Target Casino Operator Boyd Gaming appeared first on SecurityWeek.
Boyd Gaming has informed the SEC about a data breach affecting the information of employees and other individuals. The post Hackers Target Casino Operator Boyd Gaming appeared first on SecurityWeek.

Cybersecurity researchers have disclosed two security flaws in Wondershare RepairIt that exposed private user data and potentially exposed the system to artificial intelligence (AI) model tampering and supply chain risks. The critical-rated vulnerabilities in question, discovered by Trend Micro, are listed below – CVE-2025-10643 (CVSS score: 9.1) – An authenticationRead More »Two Critical Flaws Uncovered in Wondershare RepairIt Exposing User Data and AI Models
The hackers remained undetected for three weeks, deploying China Chopper, remote access scripts, and reconnaissance tools. The post GeoServer Flaw Exploited in US Federal Agency Hack appeared first on SecurityWeek.
Cybersecurity researchers believe the attack on Collins Aerospace involved a piece of ransomware known as HardBit. The post European Airport Cyberattack Linked to Obscure Ransomware, Suspect Arrested appeared first on SecurityWeek.

Most businesses don’t make it past their fifth birthday – studies show that roughly 50% of small businesses fail within the first five years. So when KNP Logistics Group (formerly Knights of Old) celebrated more than a century and a half of operations, it had mastered the art of survival. For 158Read More »How One Bad Password Ended a 158-Year-Old Business
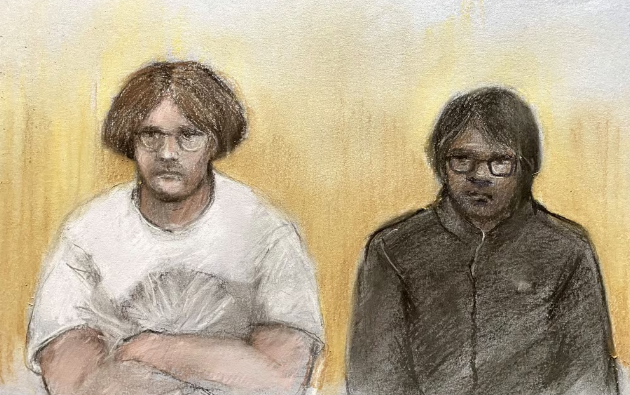
U.S. prosecutors last week levied criminal hacking charges against 19-year-old U.K. national Thalha Jubair for allegedly being a core member of Scattered Spider, a prolific cybercrime group blamed for extorting at least $115 million in ransom payments from victims. The charges came as Jubair and an alleged co-conspirator appeared inRead More »Feds Tie ‘Scattered Spider’ Duo to $115M in Ransoms

Cybersecurity researchers have disclosed details of a new malware family dubbed YiBackdoor that has been found to share “significant” source code overlaps with IcedID and Latrodectus. “The exact connection to YiBackdoor is not yet clear, but it may be used in conjunction with Latrodectus and IcedID during attacks,” Zscaler ThreatLabzRead More »New YiBackdoor Malware Shares Major Code Overlaps with IcedID and Latrodectus
This is a weird story: The US Secret Service disrupted a network of telecommunications devices that could have shut down cellular systems as leaders gather for the United Nations General Assembly in New York City. The agency said on Tuesday that last month it found more than 300 SIM serversRead More »US Disrupts Massive Cell Phone Array in New York

Think payment iframes are secure by design? Think again. Sophisticated attackers have quietly evolved malicious overlay techniques to exploit checkout pages and steal credit card data by bypassing the very security policies designed to stop them. Download the complete iframe security guide here. TL;DR: iframe Security Exposed Payment iframes areRead More »iframe Security Exposed: The Blind Spot Fueling Payment Skimmer Attacks
GitHub will implement local publishing with mandatory 2FA, granular tokens that expire after seven days, and trusted publishing. The post GitHub Boosting Security in Response to NPM Supply Chain Attacks appeared first on SecurityWeek.