

378 GB of Data From Navy Federal Credit Union Exposed
A database, in apparent association with the Navy Federal Credit Union, exposed 378 GB of information.
A database, in apparent association with the Navy Federal Credit Union, exposed 378 GB of information.
Co-founded by former MITRE experts, the startup will use the funding to accelerate product innovation and fuel company growth. The post Tidal Cyber Raises $10 Million for CTI and Adversary Behavior Platform appeared first on SecurityWeek.
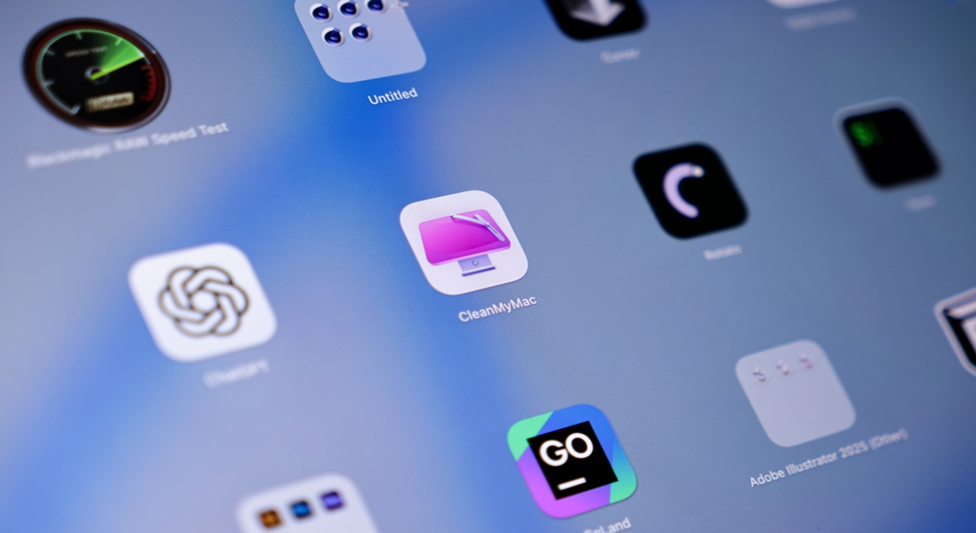
Trend™ Research analyzed a campaign distributing Atomic macOS Stealer (AMOS), a malware family targeting macOS users. Attackers disguise the malware as “cracked” versions of legitimate apps, luring users into installation.

Cybersecurity researchers have discovered two new malicious packages on the npm registry that make use of smart contracts for the Ethereum blockchain to carry out malicious actions on compromised systems, signaling the trend of threat actors constantly on the lookout for new ways to distribute malware and fly under theRead More »Malicious npm Packages Exploit Ethereum Smart Contracts to Target Crypto Developers
Flaw allows attackers to reset and hijack TP-Link TL-WA855RE devices; CISA urges users to retire discontinued extenders. The post US Cybersecurity Agency Flags Wi-Fi Range Extender Vulnerability Under Active Attack appeared first on SecurityWeek.
Chrome’s latest release addresses a high-severity use-after-free vulnerability in the V8 JavaScript engine that could be exploited for remote code execution. The post Google Patches High-Severity Chrome Vulnerability in Latest Update appeared first on SecurityWeek.
Founded in 2022 to help organizations with the secure deployment of generative-AI utilities, Aim emerged from stealth in January 2024. The post Cato Networks Acquires AI Security Firm Aim Security appeared first on SecurityWeek.

Threat actors are attempting to leverage a newly released artificial intelligence (AI) offensive security tool called HexStrike AI to exploit recently disclosed security flaws. HexStrike AI, according to its website, is pitched as an AI‑driven security platform to automate reconnaissance and vulnerability discovery with an aim to accelerate authorized redRead More »Threat Actors Weaponize HexStrike AI to Exploit Citrix Flaws Within a Week of Disclosure
A study dives into the data collected by wearable devices to better understand how it is being used.
Known for her seminal book, A Hacker Manifesto, Wark reframes hacking as a cultural force rooted in play, creativity, and human nature. The post Hacker Conversations: McKenzie Wark, Author of A Hacker Manifesto appeared first on SecurityWeek.